FEHA is certified,
just like we help you become.
View our Trust Center
ISO 27001
Certified
ISO 42001
Certified
CSA STAR
CertifiedAdd an expert team, not just a platform.
We plan, guide, and stay even after the audit.
Going it alone costs money and months.
$4.44M
Average breach cost, IBM 2025
6-12 months
To reach ISO 27001 alone
The seven steps below get most clients certified in 3-5 months.
Define your scope
Start with a clear understanding of your business, assets, processes, and compliance requirements.
Identify gaps & risks
Assess your current posture, identify control gaps, and prioritize the risks that matter most.
Manage your frameworks
Map requirements across your chosen frameworks and manage controls, policies, and evidence in one place.
Manage vendors & access
Assess third-party risks and manage access to ensure the right people and vendors have the appropriate level of access.
Monitor employee compliance
Keep track of the compliance requirements that apply to your people, including device compliance, policy acknowledgements, and background checks.
Monitor your security
Continuously identify security weaknesses across your environment with vulnerability scanning and security monitoring.
Stay audit ready
Bring everything together so your organization can track progress, resolve outstanding issues, and stay prepared for assessment.
Continuous evidence sync
Connect your entire tech stack in 60 seconds
FEHA seamlessly connects to your cloud providers, IDPs, code repositories, and HR tools via read-only connectors to automate evidence collection with zero friction.

AWS
LiveCloud

Microsoft Azure
LiveIdentity & Access
Google Cloud (GCP)
LiveCloud
Google Workspace
LiveIdentity & Access

Okta
LiveIdentity & Access

Auth0
LiveIdentity & Access

GitHub
LiveSource Code

GitLab
LiveSource Code

Bitbucket
LiveSource Code

Jira
LiveTicketing & Projects

Trello
LiveTicketing & Projects

ClickUp
LiveTicketing & Projects
BambooHR
LiveHR & People

Microsoft Intune
LiveDevice Management
Hexnode
LiveDevice Management

SecDim
UpcomingSecurity Training
Jamf
UpcomingDevice Management

MyHRToolkit
UpcomingHR & People

Kandji
UpcomingDevice Management
Two ways to run FEHA GRC
Platform only or experts included
Platform only
Do It Yourself (DIY)
Run compliance on your own terms. Full platform access: AI evidence mapping, policy drafting, automated control testing, and every framework you need. Your team stays in the driver's seat.
- For teams with in-house security or compliance capability
- Full automation from day one
- Bring experts in anytime, no replatforming
Experts included
Do For You (DFY)
A named compliance expert runs the program with you, from first gap assessment to a passed audit. Faster, lower risk, fully guided.
- ISO 27001 Lead Auditors, CISSPs, and CISMs on your file
- Pre-audit challenge and validation
- Audit support until you pass
Start either way. Add or drop experts whenever you need. Same platform, same evidence base. See pricing
Build. Comply. Prove
The infrastructure your compliance program runs on, from first control to the trust page your customers review.
Build
Cross-framework control mapping
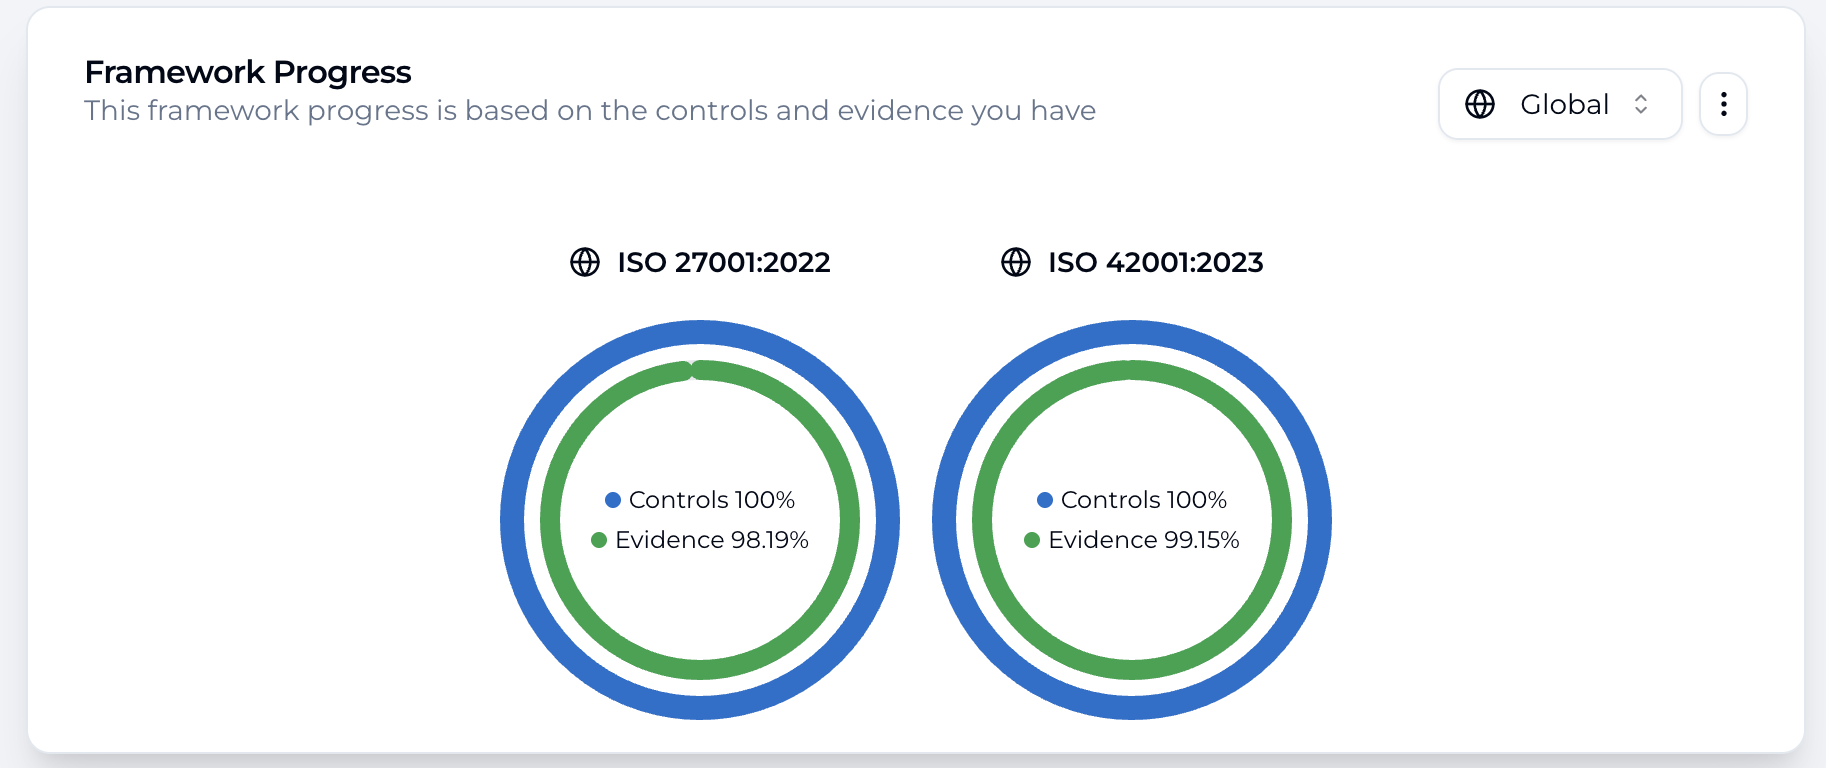
Upload your evidence once and FEHA's AI does the rest. It reads each document, learns what it proves, and maps it to every control and framework it satisfies, across ISO 27001, SOC 2, GDPR, and any framework you add later.
AI evidence mapping
Upload a document; AI matches it to every control it covers, no manual tagging.
AI evidence scoring
Each document is scored for strength, so you see the weak spots before your auditor does.
Audit-ready lineage
Every mapping is traceable, so auditors see exactly what covers what.
Build
AI policy management
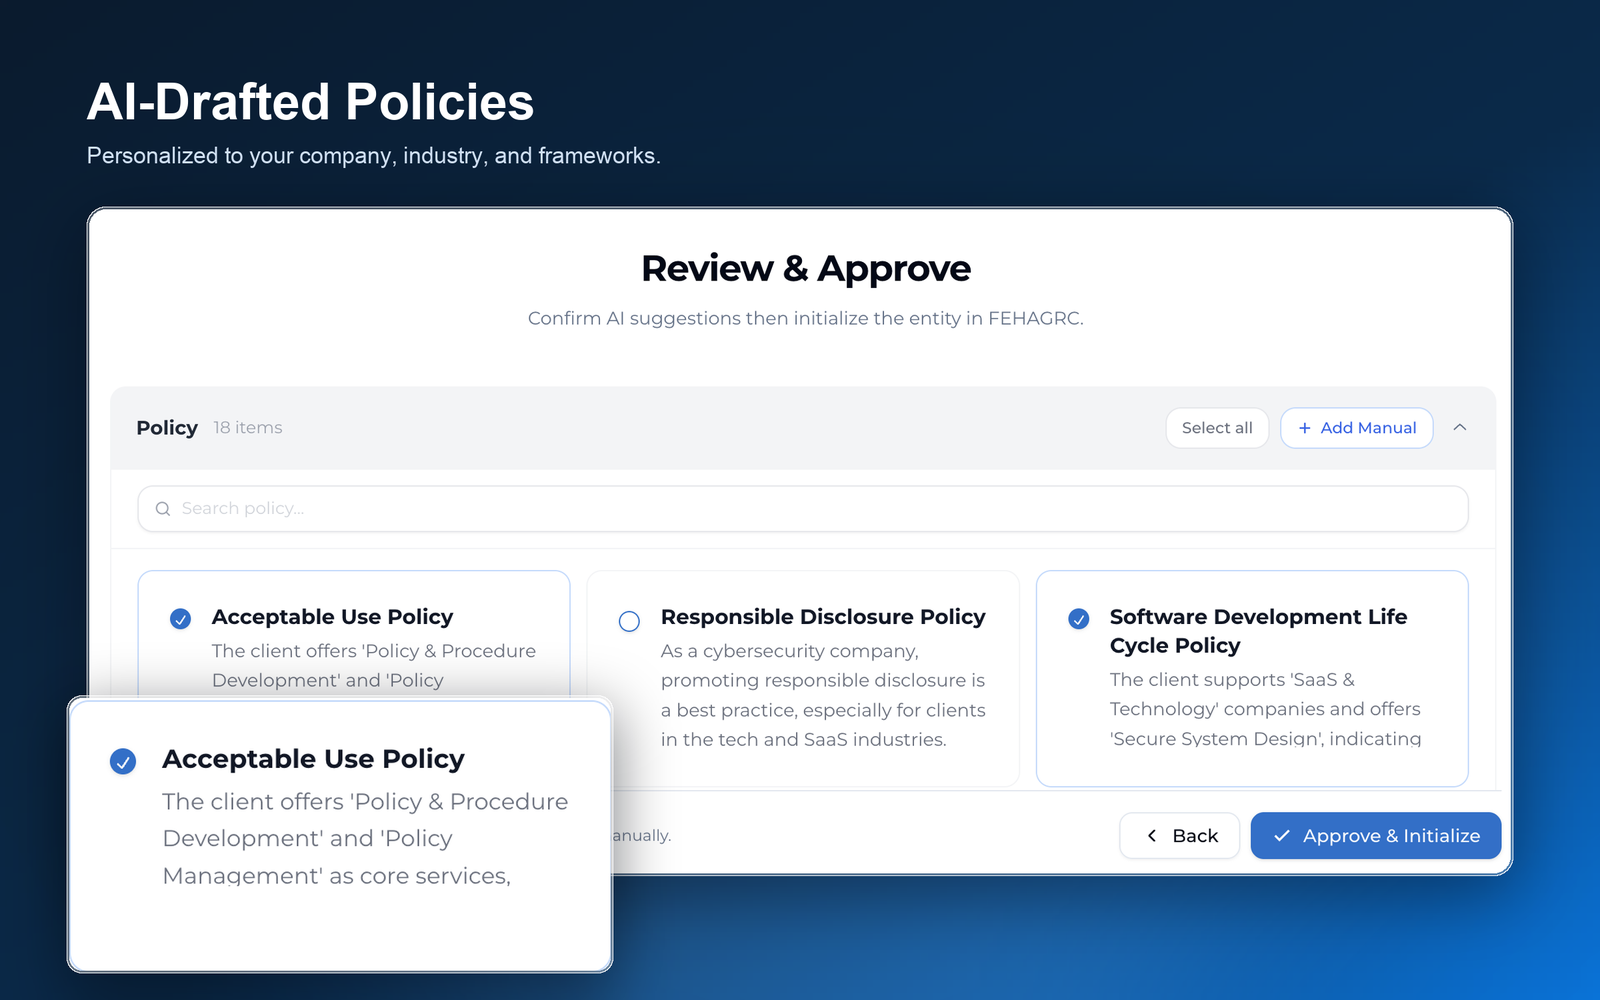
Every policy FEHA drafts is shaped by your company's profile, industry, and the frameworks you're pursuing, not a generic template. Your team edits and signs off before anything goes live, then acknowledgement campaigns and renewal reminders run on schedule.
Personalized from day one
Drafts reflect your industry, size, and frameworks from the moment you onboard.
Versioned by default
Every revision is kept with its author, date, and approver.
Staff acknowledgement
Track who has read and accepted each policy, automatically.
Build
Risk register & ranking
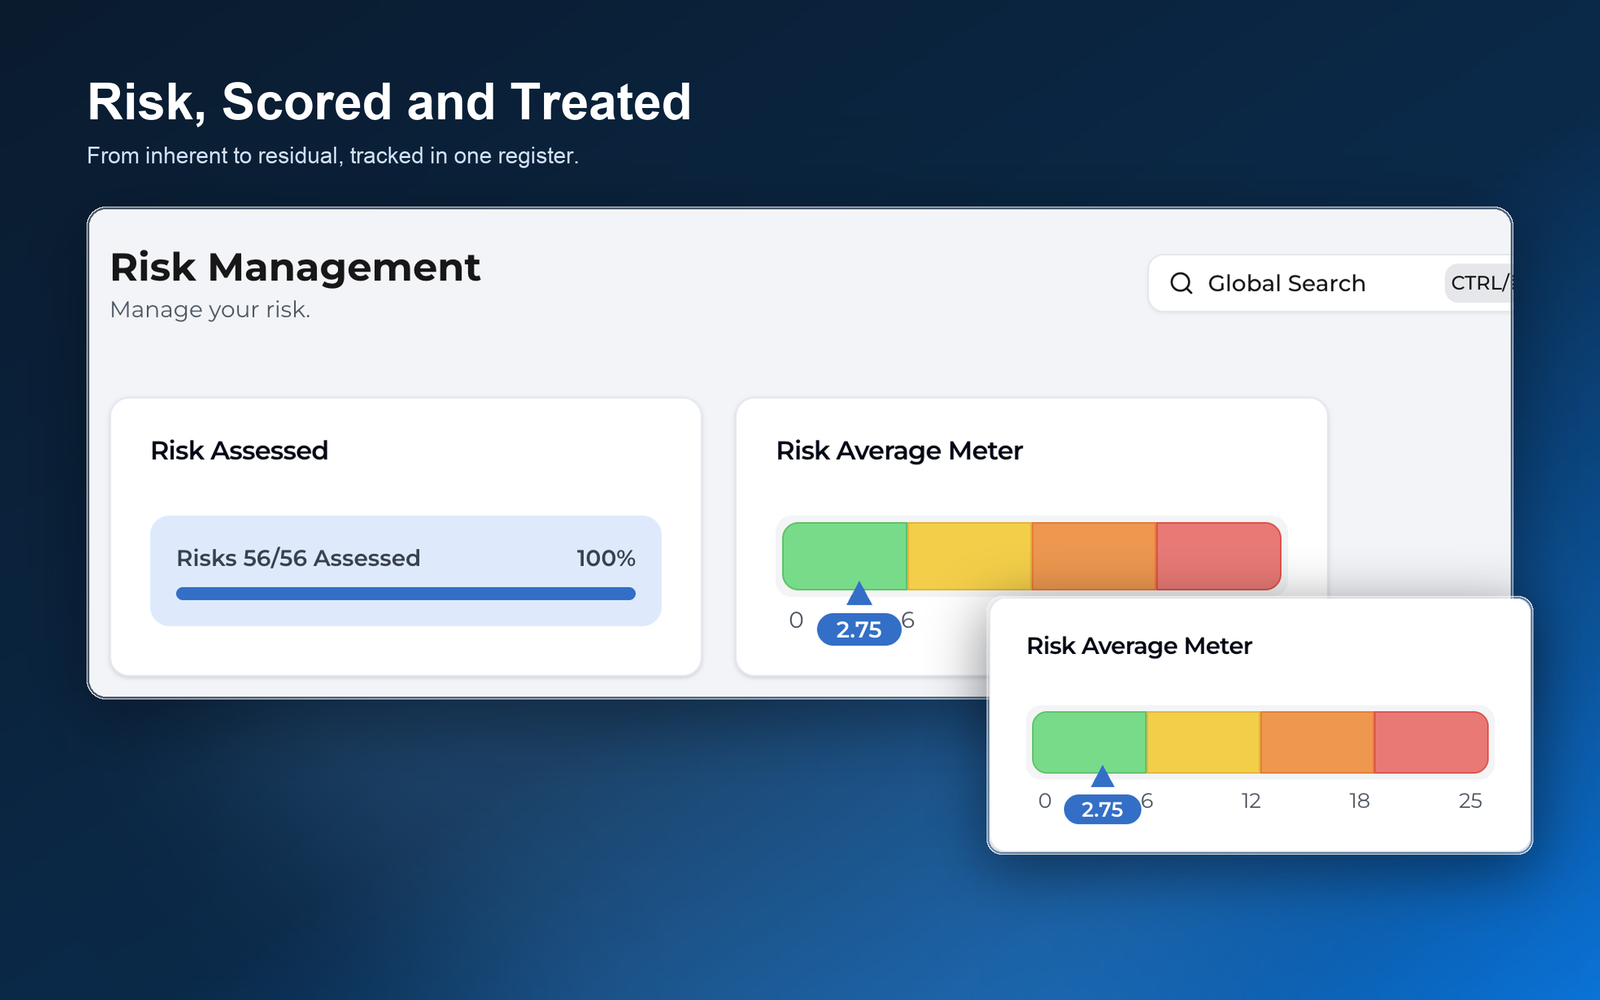
AI seeds your risk register at onboarding, scores every risk on likelihood and impact, then recommends how to treat it: accept, mitigate, transfer, or avoid. Exposure drops from inherent to residual as your team acts, tracked in one register instead of a spreadsheet.
AI-recommended risks
Your register starts populated, not blank.
Consistent scoring
Likelihood and impact scored on one shared scale across teams.
Control linkage
Mitigations map directly to controls and their evidence.
Comply
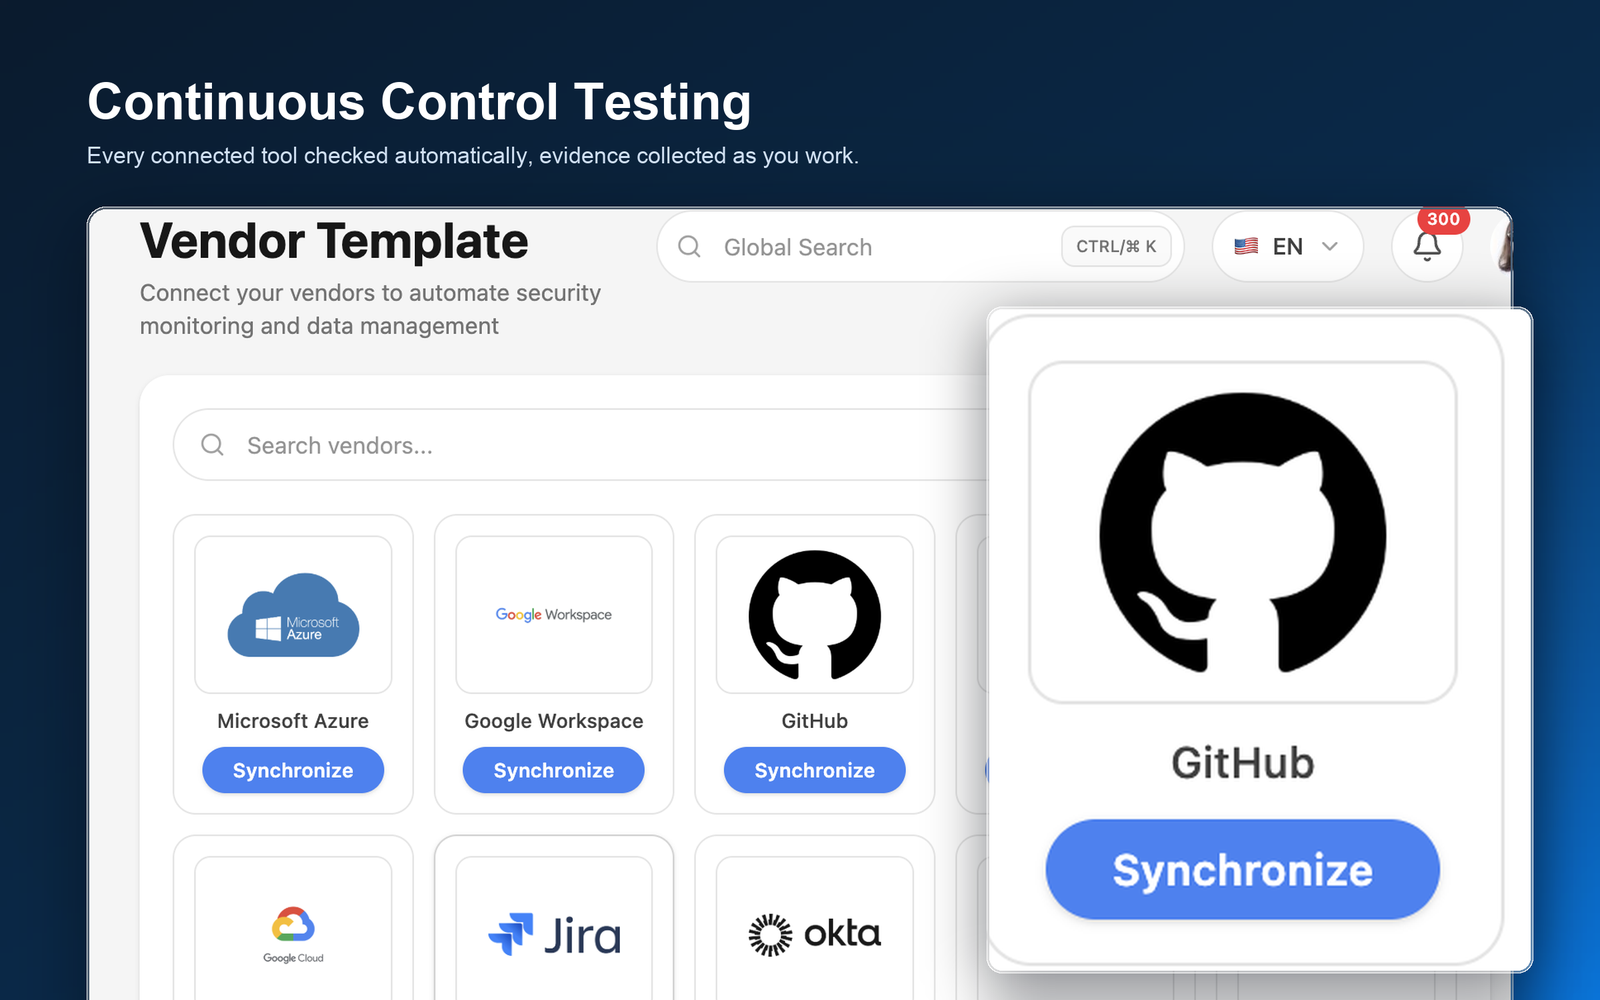
Automated control testing
FEHA connects to the tools you already run and tests your controls continuously. Evidence collects itself from your cloud, code, and identity systems, so compliance stays verified between audits, not just during them.
Continuous checks
Controls are tested automatically on a schedule; drift gets flagged the day it happens.
Evidence on autopilot
Passing checks are stored as audit evidence, mapped to the right controls.
One-click integrations
Connect your stack in minutes, with read-only access and no agents.
Works with
Comply
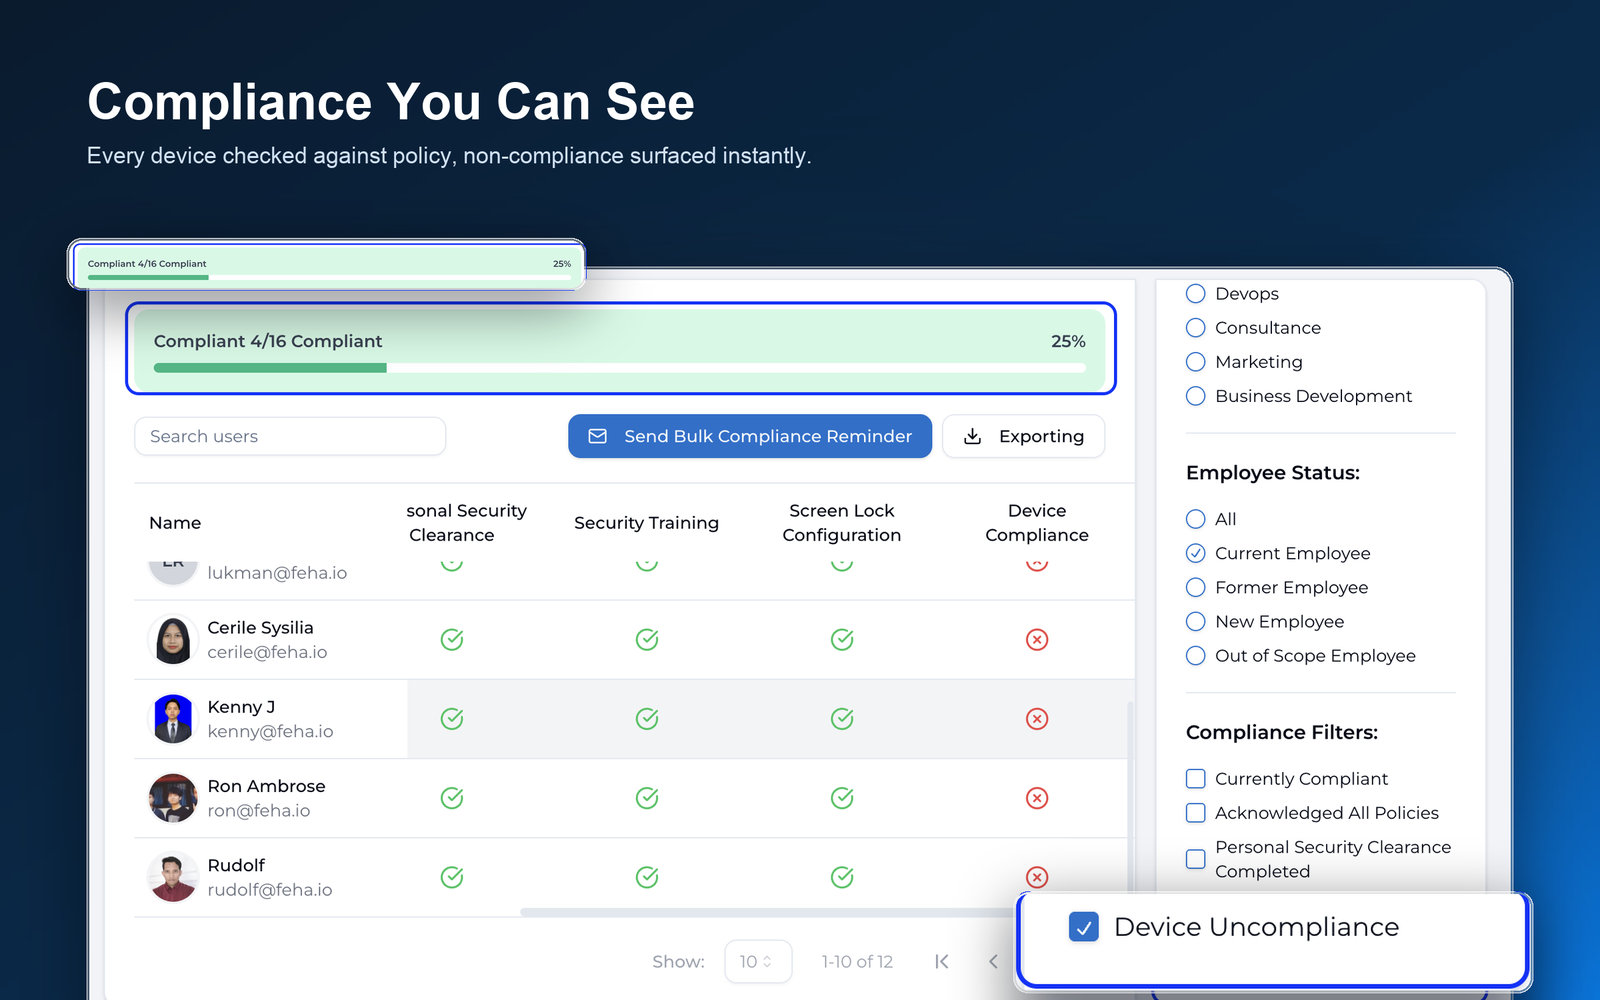
Asset & device monitoring
Keep a live view of every system and device in scope, including whether each employee's laptop still meets policy. Drift gets flagged the day it happens, not the week before an audit.
Continuous discovery
Systems and endpoints sync from your existing integrations.
Policy checks
Encryption, screen lock, and OS state verified per device.
Scope control
Mark assets in or out of scope with a documented rationale.
Comply
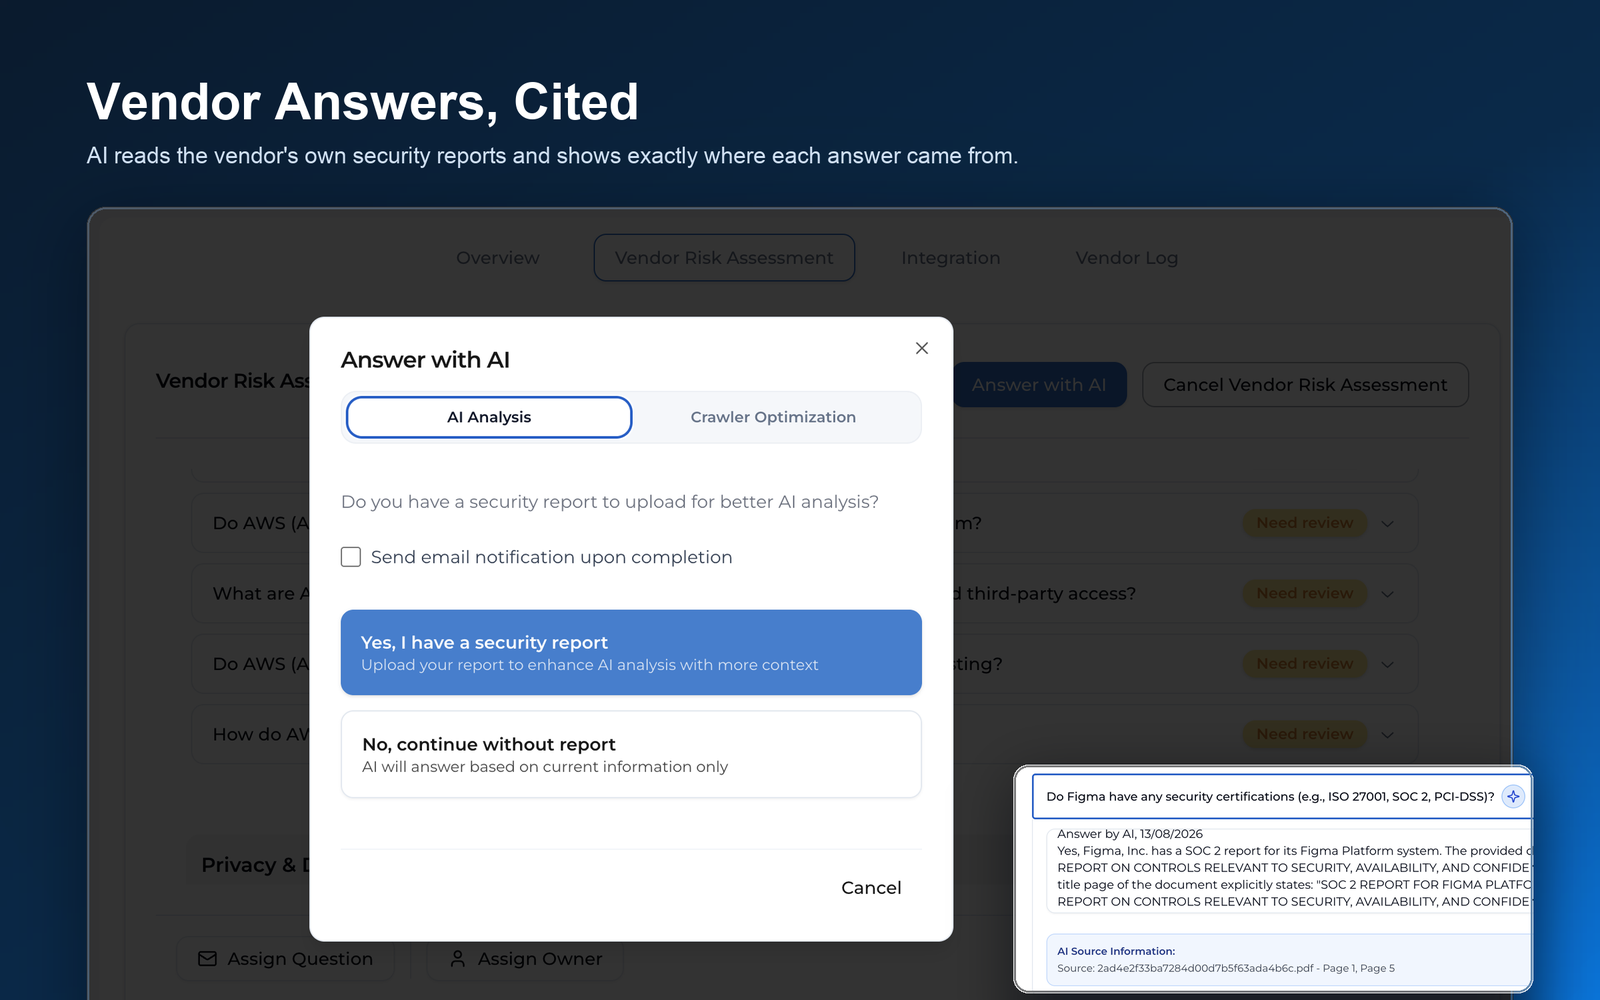
Vendor risk management
FEHA's AI reads what vendors publish, official sites, security pages, and public reports, and pre-fills their risk assessment for you to review and confirm. Follow-ups run automatically until the vendor responds.
AI vendor assessment
Assessments arrive pre-filled from public sources; you confirm instead of research.
Automated follow-up
Reminders and escalations fire without manual chasing.
Central records
Contracts, questionnaires, and scores in one vendor file.
Comply
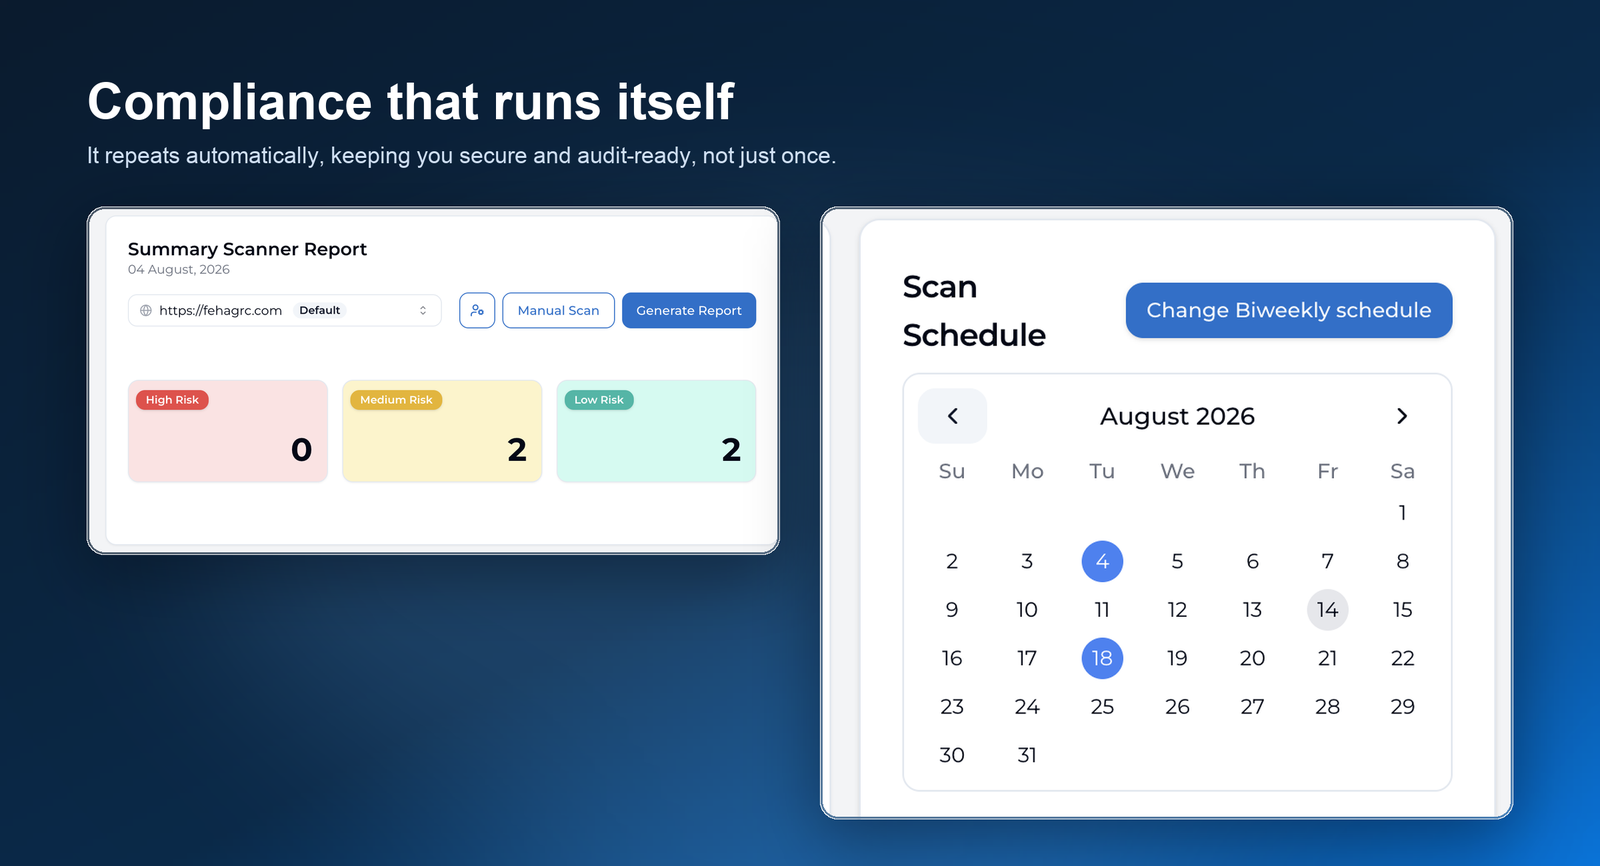
Website vulnerability scanning
Your public attack surface, scanned on a schedule. Findings come back as audit-ready reports mapped to your ISO evidence requirements, no separate security tool to buy.
Scheduled scans
Recurring external scans with no agent to deploy.
Prioritized findings
Issues ranked by severity with remediation guidance.
ISO-ready reports
Scan history doubles as audit evidence, formatted for your auditor.
Prove
Trust page
A public page that shows your compliance posture in real time. Prospects request your SOC 2 report or policies directly through it, no email thread required.
Live status
Certifications and monitoring status update automatically.
Gated documents
Reports shared under NDA with click-through approval.
Fewer questionnaires
Buyers self-serve answers before they email you.

Prove
Audit support
Compliance experts sit beside your team through audit fieldwork, answering what the checklist can't and keeping the engagement on schedule.
Named specialists
A dedicated expert who knows your program and your auditor.
Fieldwork prep
Evidence packages assembled and reviewed before requests land.
Auditor liaison
We handle clarifications so your team stays focused.
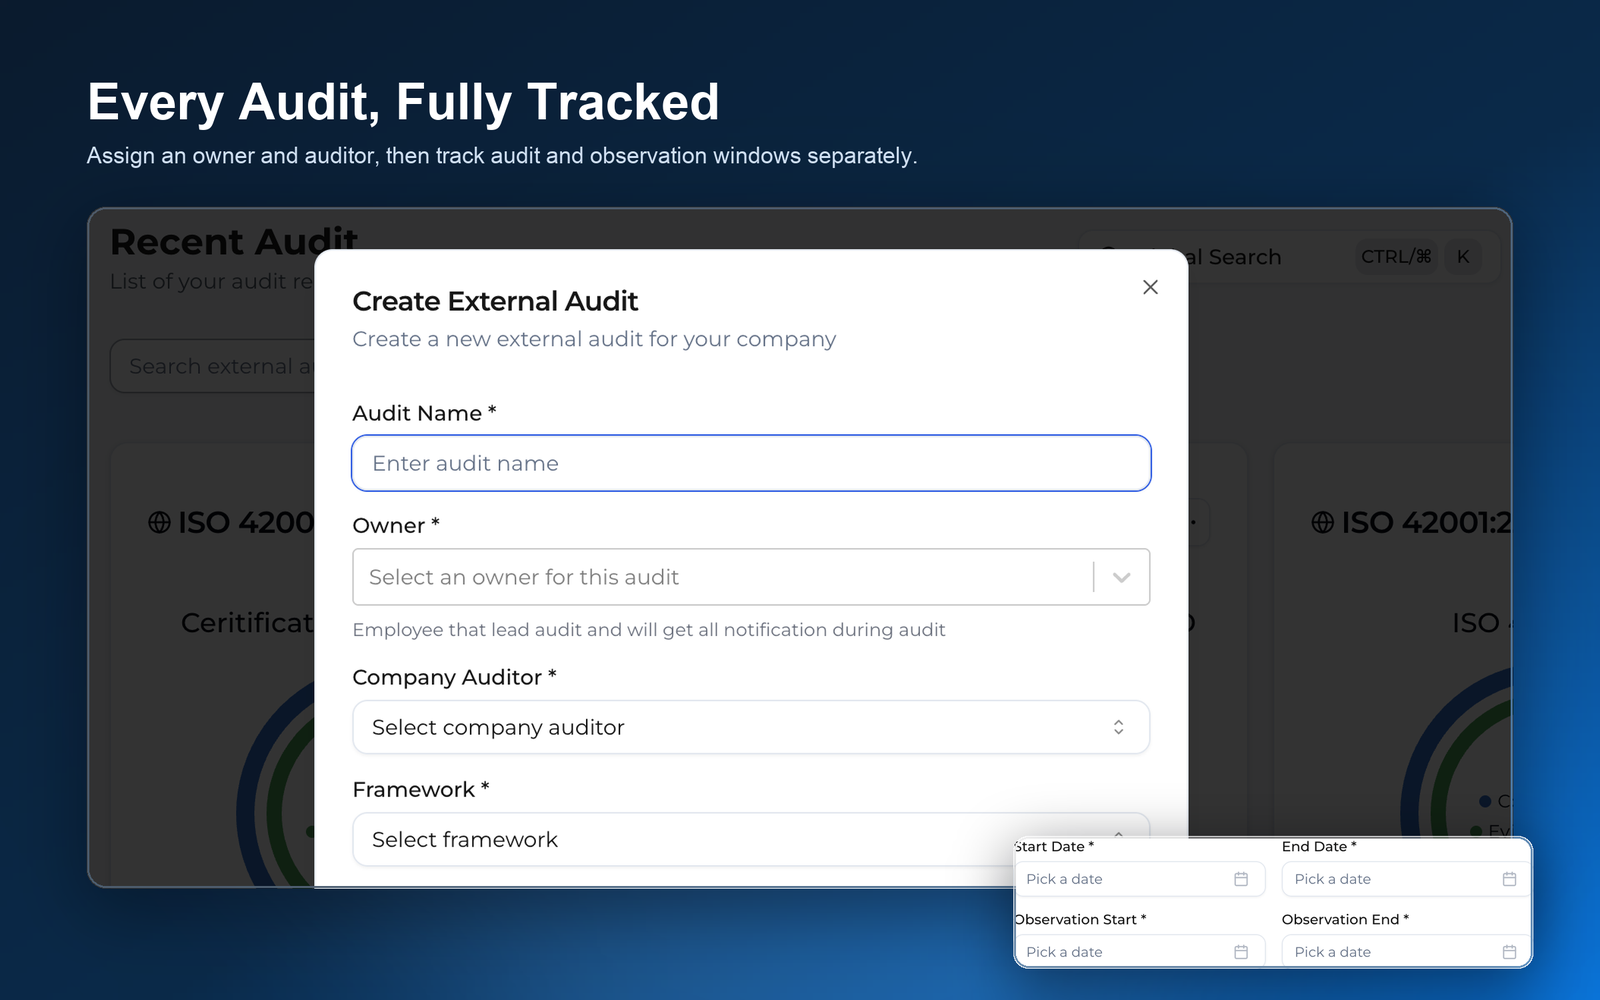
Every capability above is backed by a named compliance expert, not just a dashboard.
Wherever you operate
FEHA is more than enough!
- Global or local framework
- Startup, midmarket, or enterprise
- Finance, healthcare, AI industry, procurement, etc.
- Platform in English, Deutsch, 日本語, العربية, Bahasa Indonesia (we're adding more)
FEHA handles it all.
Don't see your country or regulations you're looking for?Talk to us
Comparison
Tools don't pass audits. The right team does
FEHA GRC runs on AI, supported by compliance experts so every gap gets caught and every fix gets done.
| Feature | FEHA GRC | Typical compliance tools |
|---|---|---|
| Platform Modules | ||
| Compliance Platform | Yes | Yes |
| Website Vulnerability Scanner | Yes | ? |
| Live Simulation (no sales call) | Yes | ? |
| Expert Support | ||
| Expert Team Available | Yes | ? |
| Pre audit Challenge & Validation | Yes | ? |
| Regional Coverage | ||
| Country & Regional Coverage | 35 frameworks across 12 coverage regions | ? |
| Localized Interface | EN · JP · AR · DE · ID | ? |
| 100% Audit Pass Rate | Yes | Not tracked |
Client Reviews & Outcomes
Enterprise trust, proven by results
Due to strict confidentiality and non-disclosure agreements, client security details remain private. Verified case studies, audit outcome reports, and reference calls are shared directly upon request.
100%
Audit Pass Rate
Every FEHA client passed their certification on the first attempt.
NDA Protected
Client Confidentiality
We protect our clients' security posture and compliance disclosures with enterprise-grade privacy.
3-5 Mos
Average Certification
From initial gap analysis to audit sign-off, guided step-by-step by certified lead auditors.
Want to see our client reviews and case studies?
Connect with our team to explore anonymized audit packages, industry-specific references, and proof of 100% first-attempt passes.
Contact us for client reviewsBlog & Resources
Simplified compliance explanation
Guides, regulatory updates, and news from the field. Clear, jargon-free, and shorter than your control list.
 compliance
Compliance Shouldn’t Be a Once-a-Year Panic
If your company’s compliance program has a season, you know the feeling. It starts with a calendar r...
Full version →
 compliance
ISO 27001, SOC 2, or PDPA? How to Decide What Your Startup Needs First
Every startup founder has had this moment. A promising deal is going well, and then the prospect’s s...
Full version →
 compliance
The Illusion of Compliance: When Your GRC Tool Only Stores Documents
Picture a compliance manager the week before an audit. Every folder is populated. Every policy is up...
Full version →
FAQ
Questions, answered
Everything you need to know
before getting started.
Your Next Audit
Compliant. Certified. Secured.
Automate governance, risk, security, and continuous compliance. Try our live simulation without an account, or book a demo with our experts.
- No account
- No doubt
- No payment
40%
Live score